Vulnerability assessments and penetration tests are often discussed together, but they answer different security questions. Treating them as interchangeable can leave an organisation with the wrong kind of assurance, unnecessary cost or gaps that nobody has actually tested.
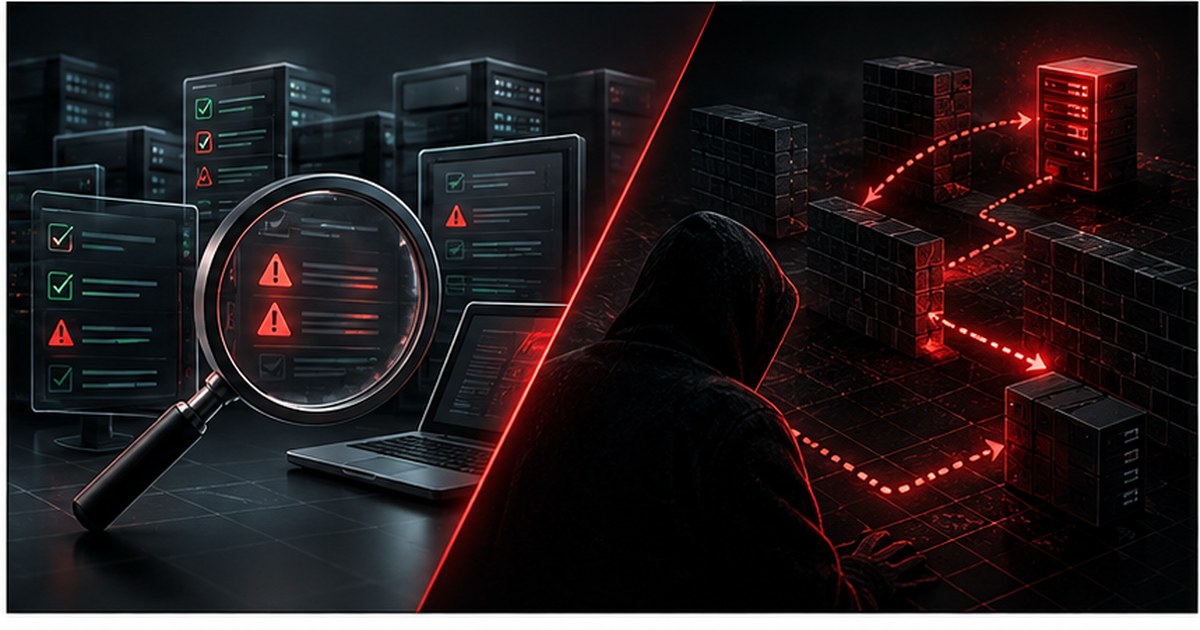
The simplest distinction is this: a vulnerability assessment is primarily concerned with identifying and prioritising weaknesses, while a penetration test goes further by using authorised attack techniques to determine whether selected weaknesses can be exploited and what an attacker could achieve.
What is a vulnerability assessment?
A vulnerability assessment reviews systems, applications or infrastructure for known security weaknesses. Automated scanning is commonly used because it can cover a large number of assets efficiently, but a useful assessment also needs validation and context.
Typical findings include missing security updates, unsupported software, exposed services, insecure protocol configurations and known vulnerabilities in installed products.
The output should help the organisation understand what is affected, severity, remediation priority and whether the finding has been validated.
What is a penetration test?
A penetration test is a controlled, authorised security assessment that simulates relevant attacker techniques against an agreed target. The objective is not to find every possible vulnerability. It is to test whether weaknesses can be combined or exploited in a way that creates meaningful security impact.
A penetration test may involve reconnaissance, manual testing, exploitation and post-exploitation activity within an agreed rules-of-engagement document. The tester should have explicit permission, a defined scope, agreed testing windows and clear restrictions on disruptive techniques.
Five important differences
1. Breadth versus depth
Vulnerability assessment is well suited to broad coverage across many systems. Penetration testing is usually narrower and deeper, concentrating human effort on selected systems, applications or attack paths.
2. Identification versus exploitation
A scanner may report that a vulnerability appears to exist. A penetration tester investigates whether it can actually be used, how far an attacker could progress and what controls limit the impact.
3. Automation versus manual judgement
Vulnerability assessment uses automation heavily. Penetration testing also uses tools, but human judgement is central to interpreting behaviour, chaining weaknesses and adapting the test as new information appears.
4. Recurring assurance versus point-in-time testing
Vulnerability scanning is particularly useful as a recurring control because environments change constantly. Penetration testing is usually performed at defined points, for example before a significant launch, after major architectural change, periodically against high-risk services or in response to a customer assurance requirement.
5. Different reporting questions
A vulnerability report should help teams prioritise and remediate weaknesses at scale. A penetration-test report should explain attack paths, demonstrated impact, evidence, risk and the remediation needed to prevent exploitation.
When should you use a vulnerability assessment?
Use vulnerability assessment when you need broad visibility, recurring identification of known weaknesses or evidence that remediation is progressing. It is particularly valuable for vulnerability-management programmes, update-management assurance and monitoring large estates.
When should you use a penetration test?
Use penetration testing when you need deeper assurance about an application, external attack surface, infrastructure segment or other defined target. It is appropriate where understanding real exploitability and attack paths matters more than simply enumerating known vulnerabilities.
They work better together
The strongest programmes do not choose one forever. Regular vulnerability management can identify and reduce known weaknesses continuously, while penetration testing provides periodic depth against systems where the consequences of compromise justify manual adversarial testing.
Findings from a penetration test can also improve the vulnerability-management programme by highlighting recurring configuration weaknesses, asset blind spots and attack paths that automated scanning did not explain.
Neither is a substitute for Cyber Essentials Plus
A general vulnerability assessment or penetration test does not replace a Cyber Essentials Plus assessment. Cyber Essentials Plus has its own defined methodology and verifies implementation of the five Cyber Essentials controls. Existing vulnerability or penetration-test evidence may be useful to the organisation's wider assurance programme, but it is not a replacement for scheme testing.
Choosing the right assessment
Start with the question you need answered. If the priority is "Where are our known weaknesses across the estate?", vulnerability assessment is usually the better starting point. If the priority is "Can an attacker exploit this system and what could they achieve?", penetration testing is the more appropriate tool.
For many organisations the answer is both, used at different frequencies and for different purposes.